Opening Statement
Project ELOHO — Active Directory Security Lab
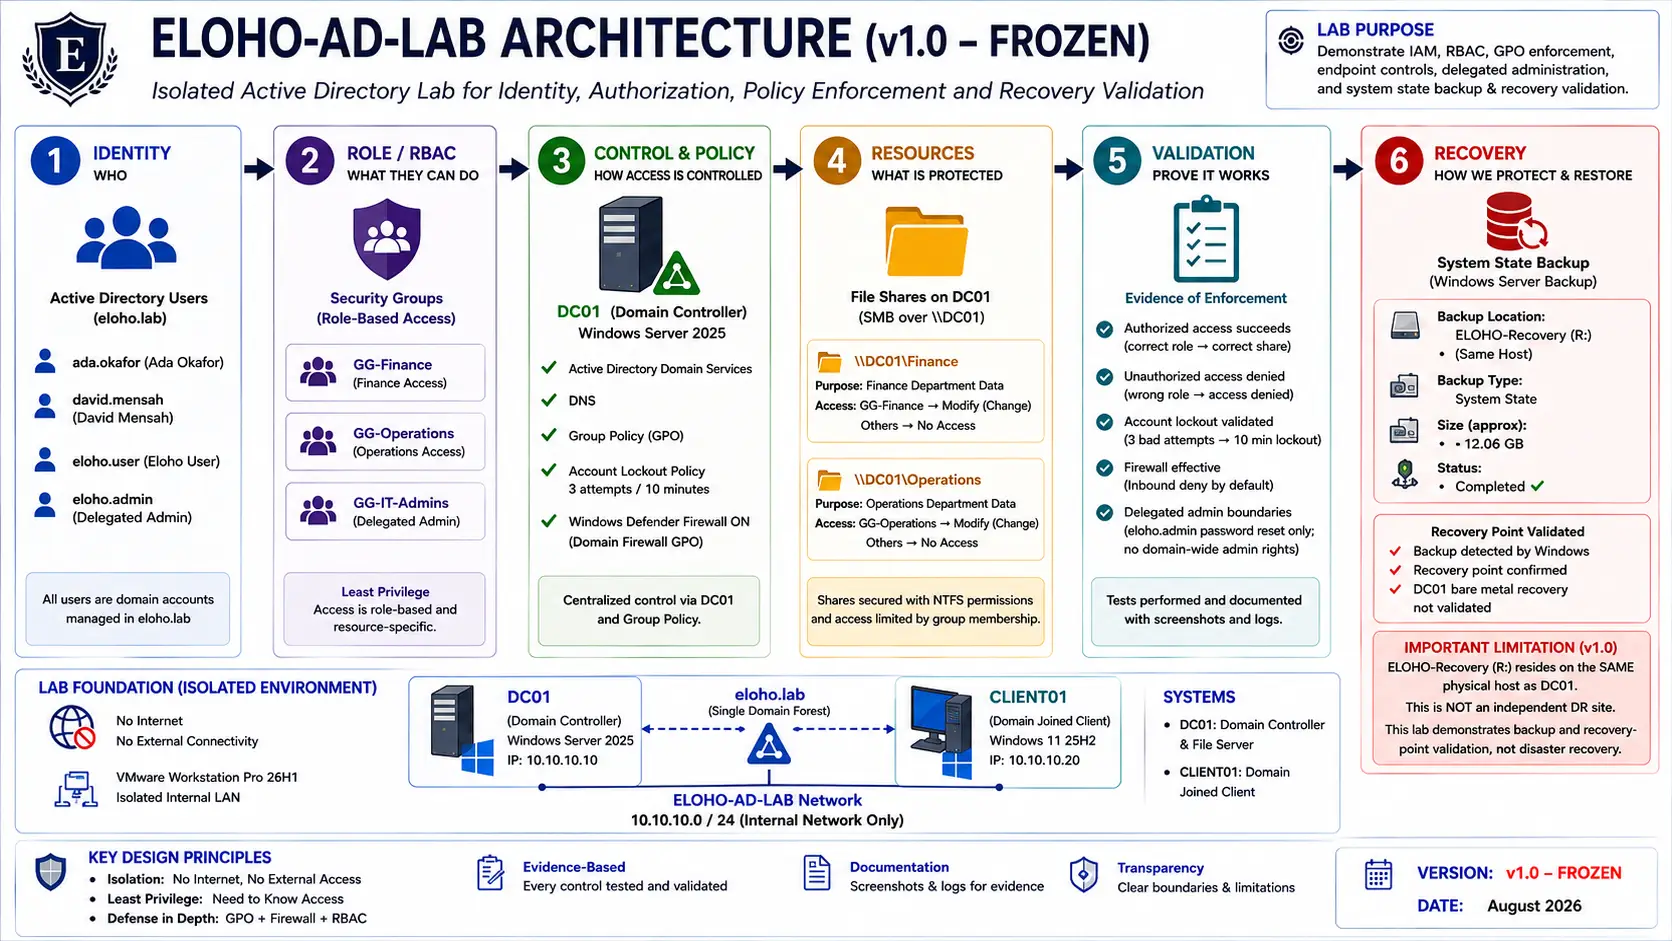
Figure 1. Project ELOHO Active Directory lab architecture showing the relationship between identity, role-based access control, policy enforcement, protected resources, validation, and recovery.
Claims Supported by Evidence
Identity and access are controlled through defined roles.
Domain identities, security groups, and NTFS/SMB permissions were implemented to enforce role-based access. Authorized users were able to access their assigned resources, while tested cross-role access was denied.
Security controls are centrally enforced and validated.
Group Policy was used to enforce workstation security controls, including account lockout and Windows Defender Firewall. Effective policy application was verified through system and command-line evidence.
Privileged access is deliberately constrained.
A separate privileged identity was granted narrowly delegated administrative authority. Password reset capability was validated, while unauthorized user creation was denied.
Recovery capability is tested within stated boundaries.
A Windows Server System State backup was completed and the recovery point was confirmed as available for System State recovery. The recovery storage resides on the same physical host and therefore represents backup and recovery-point validation, not an independent or off-site disaster recovery implementation.
Security activity is auditable and attributable.
Security auditing was configured for credential validation and file-share activity. Audit records were captured to associate tested resource access with identified domain users, providing evidence of accountability alongside access-control enforcement.
Representative Evidence
Project Evidence
The technical evidence for Project ELOHO is maintained in a structured public repository so that the implementation can be examined beyond the summary presented here. Evidence is organized across architecture, identity and role-based access control, policy enforcement, privileged access, recovery validation, and auditing and accountability. The repository includes the project architecture, representative validation evidence, and a concise technical overview of what was implemented, tested, and observed.